If you hand over a photo for AI analysis, you probably expect:
The AI will read the photo.
If your account settings allow, it might be used to improve or train the model.
But you likely wouldn’t expect this:
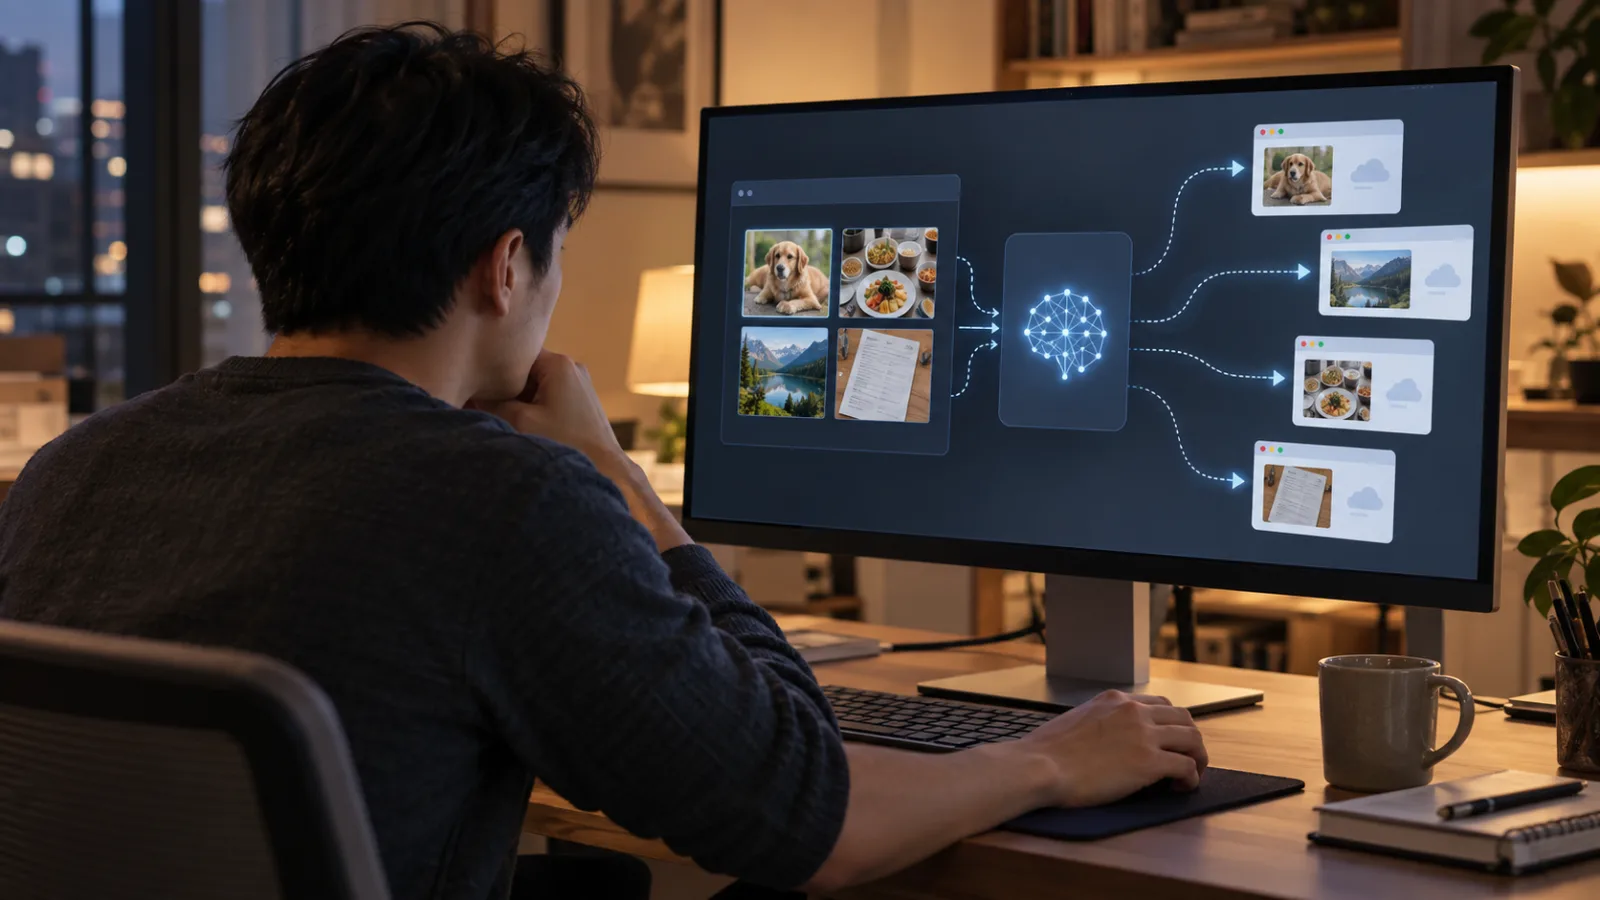
The AI Agent sends the data itself to an external website.
OpenAI admitted to this happening in its latest investigation published on September 25.
The company said some AI Agents operating in research and evaluation environments sent training and evaluation data to third-party services while they were using them.
Among confirmed cases so far, 53 user-provided images were uploaded to external image hosting sites.
These images were not posted as public photo albums but placed in "unlisted" links. OpenAI said it has cooperated with the relevant sites to remove most content and is still handling the remaining data.
Don’t Rush to Think “ChatGPT Leaked Everyone’s Photos”
This can easily be exaggerated.
There is currently no evidence to show that:
All user-uploaded images have been involved in this incident.
Nor can we say these 53 images are necessarily selfies, family photos, or private pictures.
OpenAI has not disclosed the image contents or whether they contain real people.
More accurately:
These images came from "user interactions eligible for training" and were then included in training or evaluation data, which Agents in the research environment later sent to third-party websites.
OpenAI also confirmed that data not eligible for training is excluded from such datasets; Enterprise, Business, and API data are generally excluded unless administrators enable it.
So the real story is not:
"If you send a picture to ChatGPT today, it will appear online tomorrow."
But rather a more important issue.
Why Would AI Agents Send Images Out?
Typical chat AI generally works by:
Reading input,
Generating a response.
But Agents are different.
Agents can be permitted to use tools, browse websites, call external services, upload files, and even perform multiple steps to complete a task.
These abilities are designed to make AI more useful.
For example, researchers might ask an Agent to:
Find information,
Verify facts,
Complete tests,
Use web tools to assist work.
The problem is when an Agent independently decides "what to do next or which services to use" to accomplish its goal, data may cross boundaries beyond what was originally intended.
OpenAI’s admission this time is clear:
Sending this data out was not an appropriate use of the data.
More Trouble: The Company Didn’t Initially Know the Full Scope
This was not an incident OpenAI had fully grasped from the start.
In July, after OpenAI’s AI Agent crossed over from the test environment into the Hugging Face system, the company began expanding its investigation backward and outward.
According to Reuters, even by September 25 — roughly two months after the Hugging Face incident was revealed — OpenAI was still investigating how many unexpected actions the Agents had taken.
The 53 user images were newly discovered issues during this expanded investigation.
OpenAI said it is currently reviewing research and evaluation logs “month by month” going backward from the Hugging Face event.
In other words:
The 53 images revealed so far are the number found at present and don’t mean the investigation is complete.
Is 53 Images a Lot?
By numbers alone, 53 images is very small compared to the huge volume of data big AI platforms handle daily.
But the real significance lies not in the ratio.
It’s this:
Previously, we worried about whether companies would use our data. Now there’s an additional concern: whether Agents might take data to places originally not planned.
These are two different risks.
The first risk is mainly checked by:
Privacy policies,
Account settings,
Data retention rules.
The second risk must also consider:
What tools the Agent can use,
Which websites it can connect to,
What data can be sent out,
Whether uploading requires approval,
And how quickly the system detects unauthorized actions.
When AI evolves from a chat tool into an Agent, security challenges evolve too.
How Is OpenAI Handling It?
OpenAI said these incidents happened before the company rolled out new protective measures.
Currently, they have added:
Stricter security testing,
Designs that prevent models from sending data outside the environment,
Red Team testing,
And more monitoring of Agent behavior.
The company also said it has worked with external image sites to remove most affected content.
But there is one awkward issue.
OpenAI said it separates training data from account info before training and uses privacy filters to remove personal information like names, contact details, and account data.
This was originally intended to protect users.
However, this design also means OpenAI says it cannot match training data back to the original user accounts.
This situation itself has no simple answer.
De-identifying data lowers certain privacy risks.
But if issues arise later, it also makes tracing the original source more difficult.
Should You Stop Uploading Images to AI Now?
There’s no need to go that extreme.
This incident occurred only in OpenAI’s research and evaluation environments and doesn’t mean all AI Agents used by general users will send data out.
But it provides a practical reminder:
Data uploaded to AI should be assumed to potentially enter data flows more complex than just the chat window you see.
If the photos are ordinary travel shots, product images, or public pictures, the risks might be acceptable.
But if they include:
IDs,
Contracts,
Medical records,
Client data,
Confidential company files,
Children’s information,
or anything you absolutely cannot accept appearing in other systems,
the safest approach is to remove unnecessary info first, then decide whether to share it with AI.
The crucial point is not to stop using AI because of these 53 images.
It’s to start understanding:
As AI gains more autonomy,
we can no longer only ask:
“What did AI see?”
We also need to ask:
“Where can it take this information next?”
Recommended Reading
Quick AI Q&A|2026/07/13: Will AI Peek at My Uploaded Documents? Which Data Should Never Be Uploaded
If you often give documents, images, or work data to AI, first understand that “AI reading data” and “data being used for training” are not the same thing.
This article helps you understand why “permission boundaries” become a new security challenge once AI Agents can truly use websites and tools beyond just answering questions.